
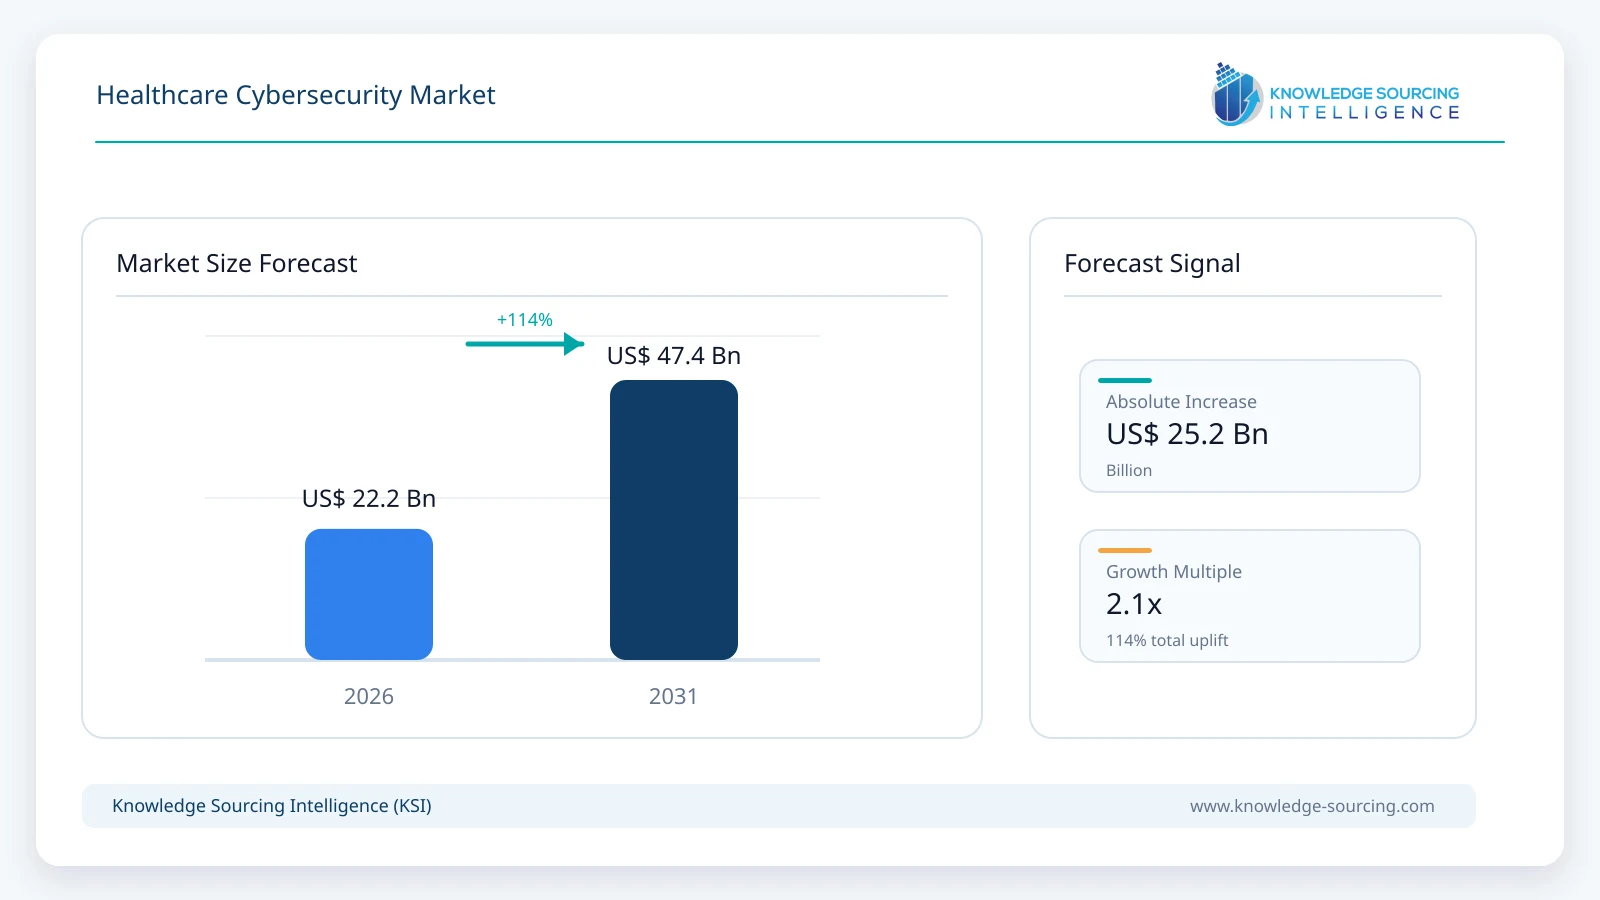
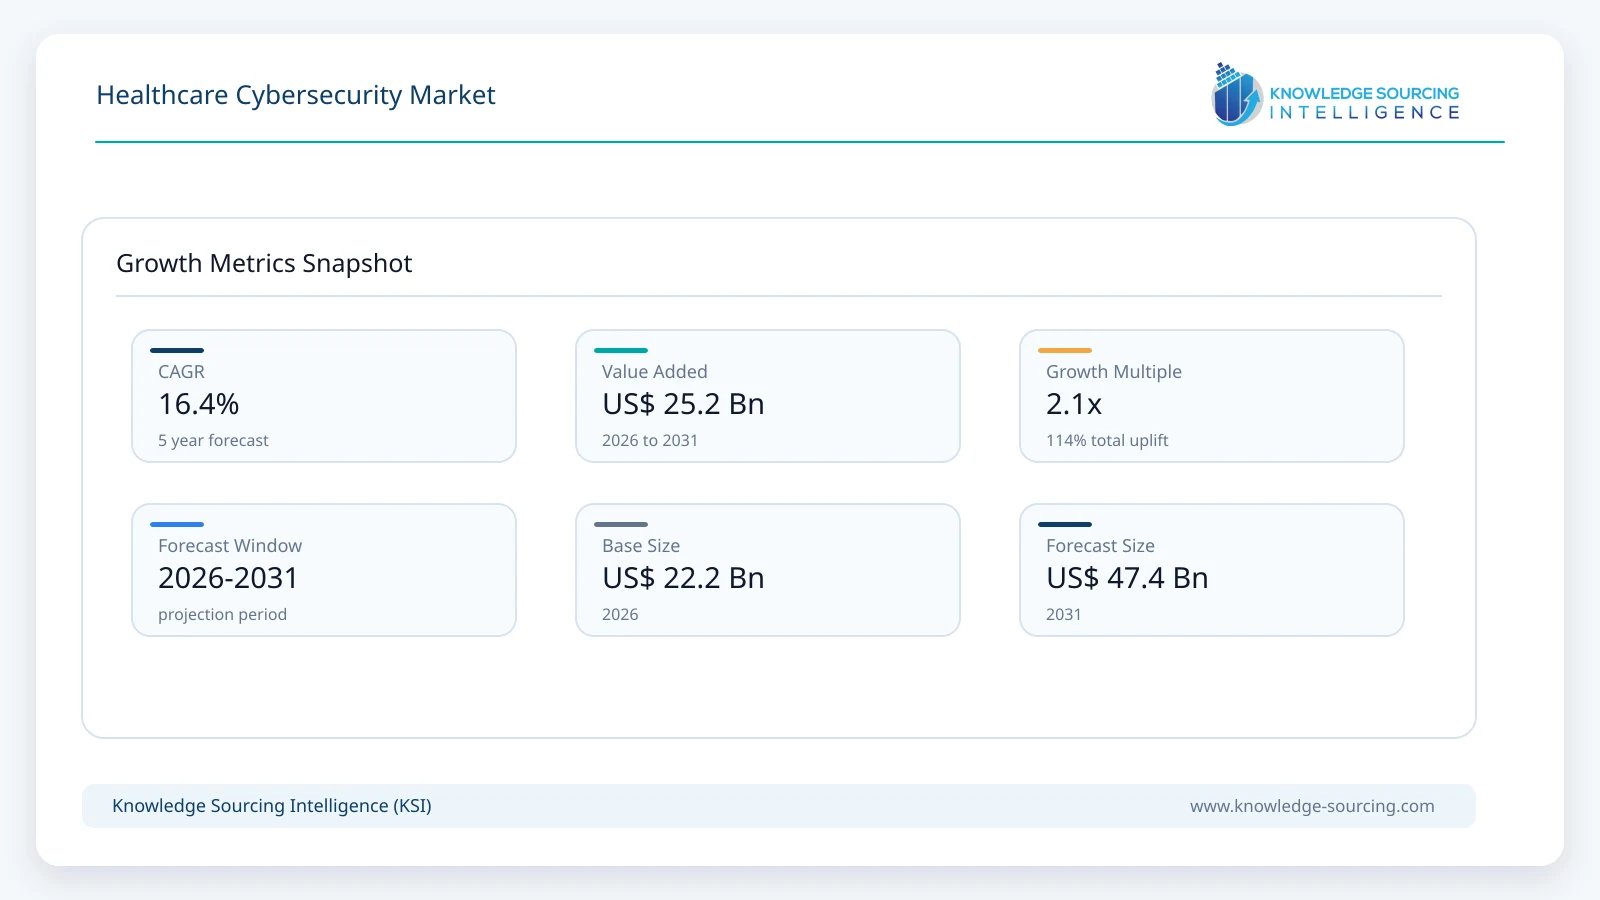
The Healthcare Cybersecurity Market is forecast to grow at a CAGR of 16.4%, reaching USD 47.4 billion in 2031 from USD 22.2 billion in 2026.
Highlights:
- 1Ransomware, credential compromise, vulnerable endpoints, and disruption of critical services are sustaining cybersecurity spending across healthcare organizations.
- 2Hospitals and healthcare providers represent a commercially important buyer group because cyber incidents can directly interrupt clinical operations and patient services.
- 3Identity and access controls are becoming central procurement priorities as healthcare environments combine on-premises systems, cloud applications, remote users, connected devices, and third-party access.
- 4North America remains an important security spending center because of extensive healthcare digitization, regulatory scrutiny, cyber-insurance requirements, and high-value patient information.
- 5European healthcare cybersecurity investment is being reinforced by coordinated EU initiatives, NIS2-related obligations, incident reporting expectations, and the European Commission's healthcare cybersecurity action plan.
- 6Medical-device cybersecurity requirements are broadening the addressable opportunity beyond enterprise IT security into product engineering, software lifecycle management, vulnerability handling, and connected-device protection.
The healthcare cybersecurity market covers technologies, platforms, and managed security capabilities used to protect healthcare information systems, connected medical devices, clinical applications, operational technology, networks, identities, and digital patient records from cyber threats. The market spans preventive, detective, and response-oriented security measures, including identity and access management, endpoint and network protection, data security, vulnerability management, security information and event management, antimalware, DDoS mitigation, and related controls.
Healthcare has a distinctive cybersecurity risk profile because security incidents can affect more than data confidentiality. A compromised clinical system can interrupt diagnostics, delay procedures, restrict access to electronic health records, disrupt pharmacy or laboratory workflows, or affect connected medical equipment. This raises the economic value of cybersecurity beyond conventional IT protection. Healthcare providers increasingly evaluate security purchases according to their ability to maintain clinical availability, protect sensitive information, satisfy regulatory obligations, and limit operational disruption.
Demand is being shaped by the expanding number of connected endpoints and the growing dependence on electronic health records, cloud applications, remote access, telemedicine platforms, diagnostic systems, connected medical devices, and third-party technology providers. Healthcare organizations also operate heterogeneous technology estates that frequently contain legacy systems, specialized equipment, and applications with long replacement cycles. This creates a larger attack surface and makes asset visibility, vulnerability management, identity controls, segmentation, and continuous monitoring important procurement priorities.
Ransomware remains one of the strongest demand catalysts. The European Commission reported that healthcare was the most targeted critical sector in the European Union in 2023, with 309 significant cybersecurity incidents reported and ransomware involved in 54% of health-sector cyberattacks. The Commission's subsequent healthcare cybersecurity action plan places greater emphasis on prevention, detection, response, and recovery.
The United States presents a similarly important demand environment. The U.S. Department of Health and Human Services has developed voluntary Healthcare and Public Health Cybersecurity Performance Goals to help organizations prioritize high-impact safeguards, including asset inventories, third-party vulnerability disclosure, identity controls, and other foundational practices. HHS has also proposed modifications to the HIPAA Security Rule to strengthen protections for electronic protected health information, increasing the importance of formal risk management and cybersecurity governance among covered entities and business associates.
Purchasing decisions are consequently moving beyond basic antivirus deployment. Larger hospitals and health systems are assessing integrated security architectures that combine identity protection, endpoint detection, network controls, vulnerability intelligence, security analytics, incident response, and data protection. Smaller providers often face a different procurement model, with managed security services, cloud-delivered protection, standardized controls, and outsourced monitoring reducing the requirement for large internal cybersecurity teams.
Pharmaceutical enterprises, medical device companies, laboratories, insurers, and other healthcare organizations create additional demand. Pharmaceutical companies must protect research data, intellectual property, manufacturing environments, and regulated information. Insurers hold extensive patient and claims data and operate large interconnected ecosystems. Medical device manufacturers must address cybersecurity across product design, premarket submissions, software maintenance, and vulnerability management. In February 2026, the U.S. Food and Drug Administration issued updated final guidance covering cybersecurity considerations for medical-device design, labeling, and premarket submissions.
The commercial structure therefore includes large cybersecurity platform vendors, network and infrastructure security suppliers, identity specialists, endpoint-security providers, device manufacturers with embedded security capabilities, and service-oriented security providers. Competition increasingly depends on the ability to integrate security controls into existing healthcare infrastructure without creating unacceptable clinical downtime or administrative burden.
Market Drivers
Increasing Financial and Operational Consequences of Ransomware
Ransomware creates a direct economic incentive for healthcare organizations to strengthen cybersecurity because an incident can simultaneously affect information availability, clinical workflows, revenue collection, and patient services. Hospitals cannot always tolerate prolonged system outages because clinical staff depend on digital systems for scheduling, documentation, imaging, laboratory coordination, medication management, and communication.
HHS enforcement activity reinforces the commercial pressure. In April 2026, the HHS Office for Civil Rights announced four settlements following ransomware investigations involving regulated healthcare entities, affecting more than 427,000 individuals. The agency stated that the resolutions brought the number of completed ransomware investigations to 19.
For buyers, this changes the purchasing equation. Security spending is increasingly evaluated against avoided downtime, regulatory exposure, recovery costs, and patient-safety risks rather than solely against the probability of data theft. Vendors that can demonstrate faster detection, containment, recovery, and system restoration can therefore compete on operational resilience as well as technical security.
Expansion of Connected Healthcare Infrastructure
Healthcare infrastructure is becoming more interconnected through electronic health records, diagnostic platforms, telehealth systems, connected medical devices, cloud workloads, mobile endpoints, remote monitoring, and external service providers. Each connection introduces authentication, software, network, data, and third-party risk.
The commercial effect is particularly relevant for hospitals operating mixed technology estates. Security teams must protect modern cloud applications while maintaining older clinical equipment and specialized systems that cannot always be patched or replaced quickly. Asset discovery, segmentation, vulnerability management, endpoint protection, and network monitoring therefore become complementary purchases rather than isolated security projects.
HHS cybersecurity performance goals specifically emphasize asset inventory and the identification of known, unknown, and unmanaged assets, illustrating the importance of visibility as a foundation for healthcare cyber risk management.
Stronger Regulatory and Compliance Requirements
Regulatory expectations are converting cybersecurity from a discretionary technology expenditure into a governance requirement. In the United States, the proposed HIPAA Security Rule amendments seek stronger cybersecurity protections for electronic protected health information. The proposal applies to covered entities and business associates, extending the compliance implications across a broad healthcare ecosystem.
The European Union is taking a coordinated approach through healthcare-specific cybersecurity initiatives. The European Commission's action plan emphasizes risk management, workforce training, detection capabilities, incident response, recovery, and sector-wide coordination.
For technology suppliers, regulation expands the buying audience. Security procurement increasingly involves compliance teams, clinical leadership, risk officers, privacy teams, procurement departments, and executive management in addition to IT security teams.
Greater Security Requirements for Medical Devices
Connected medical devices create a distinct cybersecurity spending category because device vulnerabilities can affect both information systems and clinical functions. Manufacturers must increasingly incorporate cybersecurity into product development and regulatory submissions rather than treating it solely as an after-market IT issue.
The FDA's June 2025 final guidance addressed cybersecurity in medical-device quality systems and premarket submissions, including recommendations related to device design, labeling, documentation, and statutory cybersecurity requirements. The FDA subsequently issued a February 2026 final guidance that superseded the June 2025 document.
This development expands demand for secure software engineering, threat modeling, vulnerability management, software bill-of-materials practices, security testing, product monitoring, and post-market response capabilities.
Growing Dependence on Third-Party and Digital Healthcare Ecosystems
Healthcare organizations increasingly depend on external software vendors, cloud providers, laboratories, medical-device manufacturers, billing platforms, technology service providers, and other business associates. A security weakness at one supplier can therefore create exposure for multiple healthcare customers.
Third-party risk is particularly important because healthcare organizations often cannot independently inspect every supplier's infrastructure. Procurement teams consequently place greater weight on security certifications, vulnerability disclosure processes, access controls, incident notification provisions, data-handling practices, and contractual accountability.
This favors security platforms that can provide centralized visibility across internal and external assets and supports demand for risk-management solutions that connect technical security findings with vendor and compliance workflows.
Market Restraints and Challenges
Legacy Clinical Systems and Long Replacement Cycles
Healthcare organizations frequently operate specialized systems that have long operational lifetimes. Some cannot be patched without affecting certification, interoperability, or clinical availability. Others depend on outdated software or proprietary interfaces.
The resulting security gap can limit the effectiveness of conventional endpoint and vulnerability-management programs. Buyers may need compensating controls such as network segmentation, application allowlisting, access restrictions, virtual patching, and additional monitoring. These measures add deployment complexity and can increase total ownership costs.
Cybersecurity Skills Shortages
Healthcare organizations compete with financial services, technology companies, government agencies, and other critical infrastructure operators for experienced security professionals. Smaller hospitals and specialist providers may not have sufficient personnel to maintain continuous monitoring, vulnerability assessment, threat hunting, incident response, and compliance programs.
This constraint supports managed detection and response, security operations outsourcing, cloud-based security platforms, automated alert prioritization, and security services. However, dependence on external providers also introduces third-party risk and requires effective supplier governance.
Budget Competition with Clinical Priorities
Cybersecurity budgets compete with spending on clinical equipment, hospital expansion, staffing, electronic medical records, diagnostics, pharmaceutical research, and patient-facing technologies. Security investments that do not demonstrate a clear operational or compliance outcome can face delays.
Vendors therefore need to demonstrate measurable value through reduced incident exposure, lower response times, simplified compliance, fewer security tools, or reduced staffing requirements. Integrated platforms can gain an advantage where they reduce duplicated functionality across separate security products.
Complex Procurement and Integration Requirements
Healthcare organizations often have highly fragmented technology environments. Introducing a new security platform may require integration with identity systems, electronic health records, medical devices, network infrastructure, cloud environments, security operations centers, and existing monitoring tools.
A technically capable solution can therefore lose a procurement decision if implementation risks clinical disruption or requires extensive customization. Interoperability, deployment flexibility, API availability, migration support, and managed services can become decisive commercial factors.
Security Versus Availability Trade-offs
Healthcare security controls must protect systems without interrupting patient care. Aggressive endpoint isolation, network blocking, authentication controls, or software changes can have operational consequences when applied to critical clinical systems.
Security vendors must therefore design policies that account for clinical workflows, device criticality, operating schedules, emergency access, and system dependencies. The requirement for security controls that operate with minimal disruption creates a specialized product-development challenge within healthcare.
Major Segment Analysis
Hospitals and Healthcare Providers by End User
Hospitals and healthcare providers represent the most commercially important end-user segment because they combine high-value patient information with extensive technology estates and continuous operational requirements. A large hospital can operate electronic health records, imaging systems, laboratory information systems, pharmacy systems, connected medical devices, employee endpoints, guest networks, remote-access infrastructure, cloud applications, and third-party connections within one environment.
The buyer requirement is therefore broader than data-loss prevention. Hospital security teams need to maintain system availability, restrict unauthorized access, identify compromised endpoints, detect unusual network activity, protect privileged accounts, manage vulnerabilities, and recover quickly following an incident.
Procurement is increasingly risk-based. Large healthcare systems can justify multi-layer security architectures because the financial impact of prolonged disruption can exceed the cost of prevention. They are more likely to purchase integrated endpoint, identity, network, SIEM, vulnerability-management, and response capabilities. Smaller providers may prioritize managed services and standardized cloud-based solutions because maintaining a full internal security operation can be economically difficult.
Ransomware is particularly relevant to this segment. ENISA's health-sector analysis found that healthcare providers, especially hospitals, accounted for a substantial share of analyzed incidents, while ransomware represented a leading threat category. ENISA's later threat assessments continued to identify ransomware and availability attacks as major cyber concerns.
The commercial opportunity extends across prevention and recovery. Hospitals require continuous monitoring, identity security, segmentation, endpoint controls, backup protection, vulnerability assessment, incident-response capabilities, and security governance. Suppliers that can integrate these functions while reducing alert volumes and administrative complexity are better positioned to win large healthcare contracts.
Regional Analysis
North America
North America has a mature healthcare cybersecurity purchasing environment supported by extensive electronic health record adoption, high healthcare IT spending, regulatory requirements, and a large installed base of connected medical infrastructure.
The United States represents the principal demand center. HHS initiatives, HIPAA requirements, cybersecurity performance goals, ransomware enforcement actions, and FDA medical-device cybersecurity requirements collectively influence procurement. The regulatory direction is also increasing board-level attention to cybersecurity risk.
Hospitals and health systems are prioritizing identity controls, endpoint detection, network segmentation, vulnerability management, security analytics, and incident response. Medical-device manufacturers represent an additional buyer group as cybersecurity becomes embedded into product development and regulatory processes.
Canada's demand environment is supported by digitized healthcare infrastructure and increasing attention to privacy, cyber resilience, and critical infrastructure protection. Mexico provides a developing opportunity, particularly among private healthcare networks, pharmaceutical organizations, diagnostic providers, and organizations expanding digital healthcare services. However, budget limitations and uneven cybersecurity maturity can constrain adoption outside major institutions.
Europe
Europe combines strong regulatory influence with high cybersecurity awareness among healthcare institutions. The European Commission launched a healthcare cybersecurity action plan in January 2025 following the identification of healthcare as the EU's most targeted critical sector in 2023. The plan includes prevention, detection, response, recovery, and sector-wide coordination.
The United Kingdom, Germany, France, Italy, and Spain represent major procurement markets, while other European countries contribute through national health systems, private providers, pharmaceutical companies, and medical-device ecosystems.
European buyers increasingly consider security as part of operational resilience. NIS2 requirements and related national implementation measures also influence cybersecurity governance among covered entities and their suppliers. The commercial environment favors vendors capable of supporting regulatory reporting, risk assessment, vulnerability management, incident response, and third-party security.
Asia Pacific
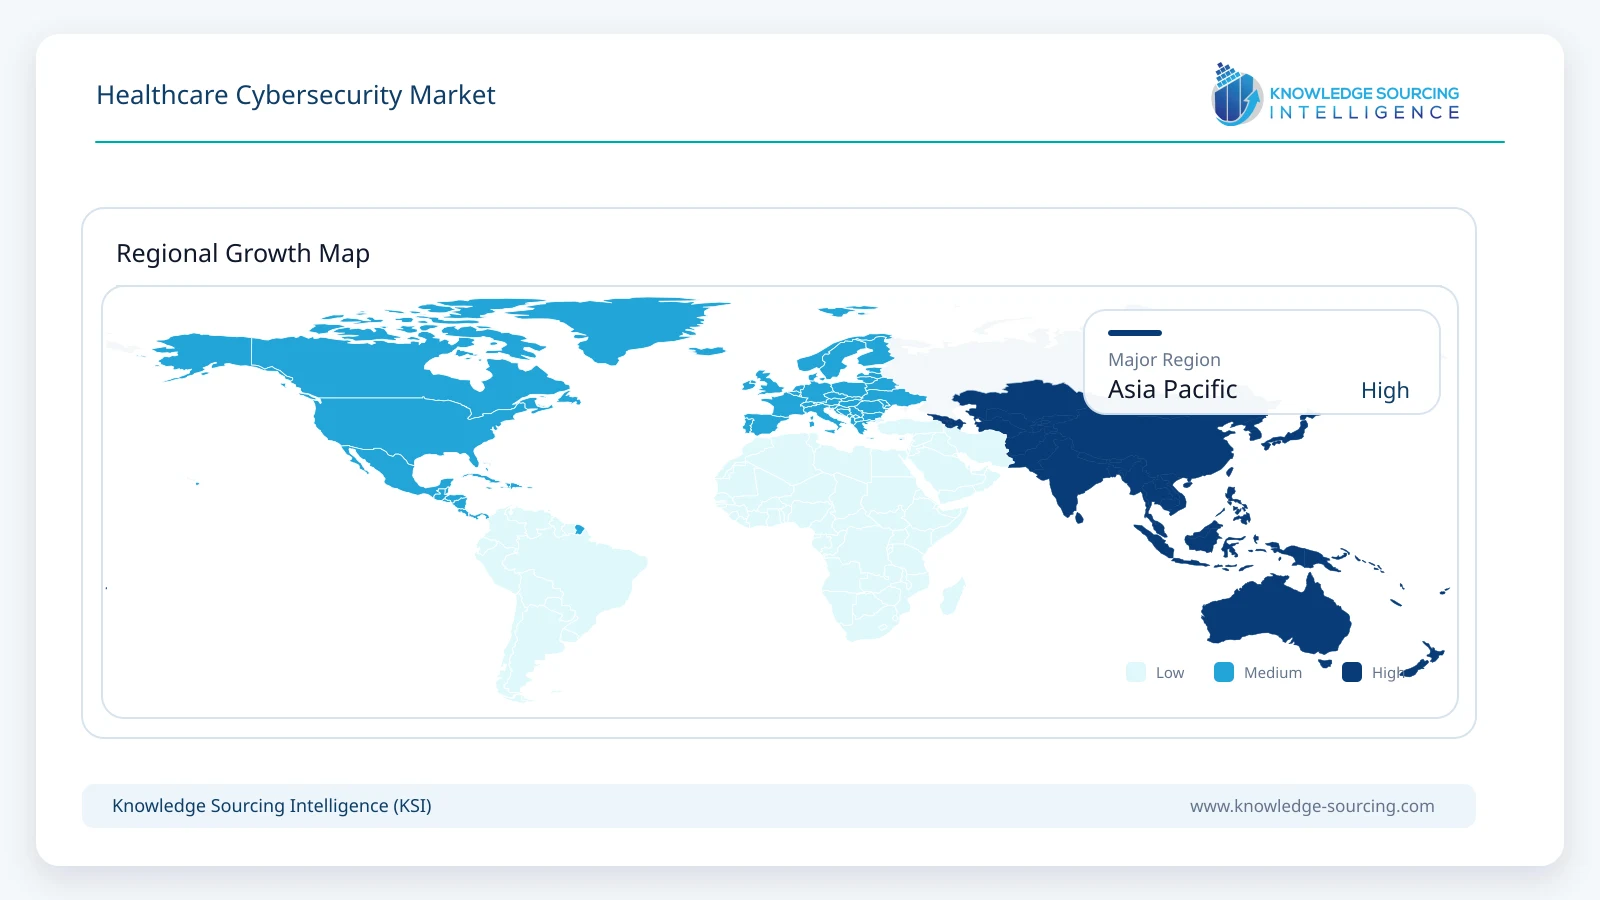
Asia Pacific combines substantial healthcare digitization with uneven cybersecurity maturity, creating a diverse procurement environment. China, Japan, India, South Korea, Taiwan, Thailand, and Indonesia each have different healthcare structures, technology adoption rates, regulatory approaches, and spending capacities.
Japan and South Korea provide relatively mature technology environments with extensive digital infrastructure and strong demand for enterprise security. China represents a large technology and healthcare ecosystem where data governance, network security, and domestic regulatory requirements influence purchasing.
India presents considerable long-term demand as hospitals, diagnostic providers, insurers, pharmaceutical companies, and digital-health platforms expand their technology infrastructure. Cost sensitivity remains important, encouraging interest in cloud-based security, managed services, automated monitoring, and solutions that can protect heterogeneous environments without requiring large internal teams.
Southeast Asian markets are developing at different speeds. Private hospital networks and digitally enabled healthcare providers can adopt advanced security controls faster than smaller institutions. Infrastructure investment, local cybersecurity expertise, regulatory maturity, and procurement budgets remain important constraints.
Middle East and Africa
Healthcare modernization programs, new hospitals, digital health initiatives, cloud adoption, and connected medical infrastructure are supporting cybersecurity demand in the Middle East. Saudi Arabia and the United Arab Emirates are particularly relevant because large healthcare investments are accompanied by stronger emphasis on digital infrastructure, data protection, and cybersecurity governance.
South Africa represents a major African cybersecurity market due to its comparatively developed private healthcare sector and broader enterprise technology ecosystem. Other African markets face greater constraints related to cybersecurity staffing, infrastructure, budgets, and legacy systems.
Regional procurement increasingly favors managed security and integrated platforms where healthcare organizations lack sufficient internal security operations capabilities.
South America
South America is developing as a healthcare cybersecurity market as hospitals, insurers, laboratories, pharmaceutical companies, and digital health providers expand electronic systems. Brazil represents the largest opportunity within the region because of its healthcare scale and extensive digital ecosystem.
Argentina and other markets provide additional opportunities, although purchasing capacity can vary substantially by institution. Economic conditions, cybersecurity staffing, fragmented healthcare infrastructure, and varying levels of technology modernization can delay adoption.
Buyers generally prioritize solutions that address immediate exposure, including endpoint security, identity management, ransomware prevention, data protection, and vulnerability management. Cloud-delivered security can support adoption where local infrastructure and specialist personnel are limited.
Competitive Landscape
The healthcare cybersecurity market contains several overlapping competitive groups rather than a single standardized vendor structure. Enterprise cybersecurity platforms compete with specialist identity providers, network-security vendors, endpoint-security suppliers, application and data protection companies, infrastructure technology firms, and healthcare technology manufacturers.
The competitive set supplied for this market includes Broadcom Inc., Trend Micro Incorporated, Cisco Systems, Inc., International Business Machines Corporation (IBM), Kaspersky, Trellix, Intel Corporation, GE HealthCare, CrowdStrike Holdings, Inc., Imperva, Inc., CyberArk Software Ltd., and Palo Alto Networks, Inc..
Competition is shaped by platform breadth, detection accuracy, integration capabilities, threat intelligence, identity protection, endpoint visibility, network security, cloud security, incident response, and the ability to operate across complex healthcare environments. Buyers increasingly prefer architectures that consolidate multiple controls while retaining compatibility with existing healthcare applications and devices.
Partnerships are commercially important because healthcare cybersecurity often crosses organizational boundaries. Security suppliers can work with cloud providers, healthcare technology vendors, managed service providers, medical-device manufacturers, systems integrators, and healthcare institutions to improve deployment and expand account reach.
Expansion strategies are also moving toward platform integration. Vendors with established network, endpoint, identity, data, or security analytics products can cross-sell additional controls into existing healthcare accounts. Specialist vendors can compete by providing deeper capabilities in areas such as identity protection, endpoint detection, application security, or privileged access.
GE HealthCare occupies a differentiated position within the competitive set because its healthcare technology portfolio gives it direct exposure to clinical equipment and hospital workflows. This creates an opportunity to integrate cybersecurity considerations more closely with medical-device and clinical-system requirements.
Overall, competitive differentiation is shifting from individual security features toward breadth of coverage, interoperability, healthcare-specific deployment expertise, response capabilities, regulatory support, and total cost of ownership.
Recent Developments
April 2026: The U.S. HHS Office for Civil Rights announced four HIPAA Security Rule ransomware settlements involving more than 427,000 affected individuals. Commercial relevance: Continued enforcement raises the cost of inadequate risk management and strengthens the business case for ransomware prevention, security monitoring, access controls, and documented cybersecurity governance.
March 2026: MedSec launched BRIDGE, a centralized platform connecting medical device manufacturers and healthcare delivery organizations to streamline sharing of critical medical device cybersecurity information.
February 2026: Fortified Health Security launched TPRM with VendorIQ, a healthcare-specific third-party risk management solution integrating automated workflows, real-time assessment tracking, and expert risk insights within its Central Command platform.
June 2025: The U.S. FDA issued final guidance on cybersecurity in medical devices covering quality-system considerations and cybersecurity information recommended for premarket submissions. Commercial relevance: Medical-device manufacturers must place greater emphasis on cybersecurity throughout product development and regulatory preparation, expanding demand for security engineering and vulnerability-management capabilities.
Regulatory and Policy Environment
Healthcare cybersecurity is governed by a combination of privacy regulation, critical-infrastructure requirements, medical-device rules, cybersecurity frameworks, breach-notification obligations, and national security policies.
In the United States, HIPAA remains a central regulatory framework for protecting electronic protected health information. HHS's December 2024 proposed Security Rule amendments seek stronger technical and organizational safeguards, reflecting the increasing policy focus on cybersecurity risk within healthcare. HHS has also developed voluntary Healthcare and Public Health Cybersecurity Performance Goals that provide organizations with prioritized practices for improving cyber preparedness and resilience.
Medical devices are subject to additional cybersecurity expectations. Section 524B of the U.S. Federal Food, Drug, and Cosmetic Act established cybersecurity requirements for certain cyber devices, while FDA guidance provides recommendations for device design, labeling, premarket submissions, and cybersecurity risk management. The February 2026 final guidance is the latest FDA guidance identified for this area in the supplied research period.
In Europe, cybersecurity policy is becoming more coordinated across the healthcare sector. The European Commission's healthcare cybersecurity action plan emphasizes preparedness, risk management, detection, response, recovery, and cooperation among healthcare providers, Member States, ENISA, and cybersecurity stakeholders.
ENISA also provides sector-specific guidance and threat intelligence. Its 2025 health-sector cyber-hygiene guidance addresses practical measures for organizations ranging from large hospitals to smaller clinics and general practitioners. The agency's 2025 threat landscape analyzed 4,875 incidents covering July 2024 through June 2025, providing a broader basis for understanding European cyber-risk patterns.
Regulatory requirements influence the market through several purchasing channels. Organizations must demonstrate appropriate safeguards, maintain incident-response processes, manage vulnerabilities, protect sensitive information, monitor third parties, and increasingly incorporate cybersecurity into medical-device development. This shifts cybersecurity procurement toward solutions that generate auditable controls and measurable risk-management outcomes.
Outlook and Strategic Implications
Healthcare cybersecurity spending through 2031 will be influenced less by the number of individual attacks alone and more by the economic consequences of system disruption, regulatory enforcement, interconnected healthcare infrastructure, and the increasing security requirements attached to medical devices and external technology providers.
Identity security is likely to remain a core investment area as healthcare environments become more distributed. Authentication, privileged access, least-privilege controls, credential monitoring, and lifecycle management are increasingly important because compromised identities can provide attackers with direct access to clinical and administrative systems.
Ransomware defense will remain a major procurement priority, but buyers are likely to demand broader resilience rather than relying solely on malware prevention. Endpoint visibility, network segmentation, immutable recovery capabilities, vulnerability management, threat detection, incident response, and tested recovery procedures will increasingly be evaluated as interconnected controls.
Security operations will also become more automated. Healthcare organizations facing staffing limitations will seek platforms capable of reducing alert volumes, correlating events, prioritizing vulnerabilities, identifying suspicious behavior, and supporting faster response. Artificial intelligence may contribute to security analytics and investigation workflows, but healthcare buyers will continue to evaluate accuracy, explainability, data handling, integration, and operational risk.
Medical-device cybersecurity represents an expanding strategic opportunity. The integration of cybersecurity into regulatory submissions and product lifecycle management means manufacturers need capabilities that extend from design-stage threat assessment through post-market vulnerability management. This creates opportunities for suppliers that can connect enterprise cybersecurity with specialized medical-device requirements.
Procurement will increasingly include third-party risk. Hospitals depend on business associates, cloud providers, device manufacturers, software suppliers, and other external organizations, making supplier security a material part of enterprise risk management. Vendors that provide centralized visibility across internal and external assets can address this requirement more effectively than isolated point solutions.
The competitive environment will consequently favor security providers that can demonstrate measurable protection across multiple layers while fitting healthcare's operational constraints. Platform consolidation can reduce administrative complexity, but buyers will continue to demand interoperability because healthcare organizations rarely operate homogeneous technology estates.
Regional strategies will also diverge. North American suppliers and buyers will remain strongly influenced by HIPAA, HHS initiatives, ransomware enforcement, and medical-device regulation. European procurement will be shaped by coordinated healthcare cybersecurity policies, NIS2-related requirements, and ENISA guidance. Asia Pacific will present a mix of mature enterprise-security demand and infrastructure modernization opportunities. Middle Eastern markets will benefit from healthcare investment and national cybersecurity programs, while South American markets will remain sensitive to institutional budgets and technology maturity.
For healthcare providers, the strategic priority is moving from isolated security products toward measurable cyber resilience. For cybersecurity vendors, the opportunity lies in reducing deployment complexity, integrating with clinical environments, supporting regulatory requirements, and demonstrating operational outcomes. For medical-device manufacturers, cybersecurity must increasingly be treated as a product lifecycle responsibility rather than a separate IT function.
The next five years will therefore be shaped by the intersection of patient safety, operational continuity, regulatory accountability, connected-device exposure, identity security, ransomware resilience, and third-party risk. Healthcare organizations that can align cybersecurity investment with clinical continuity and measurable risk reduction will be better positioned to justify sustained security budgets, while suppliers that understand the operational constraints of healthcare will have stronger opportunities to convert cybersecurity requirements into long-term commercial relationships.
Healthcare Cybersecurity Market Scope:
| Report Metric | Details |
|---|---|
| Total Market Size in 2026 | USD 22.2 billion |
| Total Market Size in 2031 | USD 47.4 billion |
| Forecast Unit | Billion |
| Growth Rate | 16.4% |
| Study Period | 2021 to 2031 |
| Historical Data | 2021 to 2024 |
| Base Year | 2025 |
| Forecast Period | 2026 – 2031 |
| Segmentation | Type of Threat, Solution, End User, Geography |
| Companies |
|
Market Segmentation
By Type of Threat
Ransomware
Malware
Phishing and Social Engineering
Distributed Denial of Service (DDoS)
Advanced Persistent Threats (APTs)
Insider Threats
Data Breaches and Unauthorized Access
Other Threats
By Solution
Network Security
Endpoint Security
Identity and Access Management
Cloud Security
Data Security and Privacy
Security Information and Event Management (SIEM) and Security Operations
Risk, Compliance and Governance
Medical Device and IoMT Security
Vulnerability Management
Other Solutions
By End-User
Hospitals and Healthcare Providers
Pharmaceutical and Biotechnology Companies
Health Insurance Companies and Payers
Diagnostic Laboratories
Medical Device Manufacturers
Clinics and Ambulatory Care Centers
Digital Health and Telehealth Providers
Other Healthcare Organizations
By Geography
North America
USA
Canada
Mexico
South America
Brazil
Argentina
Others
Europe
United Kingdom
Germany
France
Italy
Spain
Others
Middle East and Africa
Saudi Arabia
UAE
Others
Asia Pacific
China
Japan
India
South Korea
Taiwan
Thailand
Indonesia
Others
Table of Contents
1. EXECUTIVE SUMMARY
2. MARKET SNAPSHOT
2.1. Market Overview
2.2. Market Definition
2.3. Scope of the Study
2.4. Market Segmentation
3. BUSINESS LANDSCAPE
3.1. Market Drivers
3.2. Market Restraints
3.3. Market Opportunities
3.4. Porter’s Five Forces Analysis
3.5. Industry Value Chain Analysis
3.6. Regulatory and Policy Landscape
3.7. Strategic Recommendations
4. TECHNOLOGY ANALYSIS AND OUTLOOK
4.1. Artificial Intelligence and Machine Learning in Healthcare Cybersecurity
4.2. Zero Trust Security
4.3. Endpoint Detection and Response
4.4. Security Information and Event Management
4.5. Cloud Security
4.6. Medical Device and IoT Security
4.7. Other Technologies
5. HEALTHCARE CYBERSECURITY MARKET BY TYPE OF THREAT
5.1. Introduction
5.2. Malware
5.3. Ransomware
5.4. Distributed Denial of Service (DDoS)
5.5. Advanced Persistent Threats (APTs)
5.6. Spyware
5.7. Phishing and Social Engineering
5.8. Lost or Stolen Devices
5.9. Others
6. HEALTHCARE CYBERSECURITY MARKET BY SOLUTION
6.1. Introduction
6.2. Identity and Access Management
6.3. Risk and Compliance Management
6.4. Endpoint Security
6.5. Network Security
6.6. Data Security
6.7. Antivirus and Antimalware
6.8. DDoS Mitigation
6.9. Security Information and Event Management
6.10. Vulnerability Management
6.11. Others
7. HEALTHCARE CYBERSECURITY MARKET BY END USER
7.1. Introduction
7.2. Hospitals and Healthcare Providers
7.3. Pharmaceutical Enterprises
7.4. Health Insurance Providers
7.5. Laboratories and Diagnostic Centers
7.6. Medical Device Companies
7.7. Other Healthcare Organizations
8. HEALTHCARE CYBERSECURITY MARKET BY GEOGRAPHY
8.1. Introduction
8.2. North America
8.2.1. United States
8.2.2. Canada
8.2.3. Mexico
8.3. South America
8.3.1. Brazil
8.3.2. Argentina
8.3.3. Others
8.4. Europe
8.4.1. United Kingdom
8.4.2. Germany
8.4.3. France
8.4.4. Italy
8.4.5. Spain
8.4.6. Others
8.5. Middle East and Africa
8.5.1. Saudi Arabia
8.5.2. United Arab Emirates
8.5.3. South Africa
8.5.4. Others
8.6. Asia Pacific
8.6.1. China
8.6.2. Japan
8.6.3. India
8.6.4. South Korea
8.6.5. Taiwan
8.6.6. Thailand
8.6.7. Indonesia
8.6.8. Others
9. COMPETITIVE ENVIRONMENT AND ANALYSIS
9.1. Major Players and Strategy Analysis
9.2. Market Share Analysis
9.3. Mergers, Acquisitions, Agreements, and Collaborations
9.4. Competitive Dashboard
10. COMPANY PROFILES
10.1. Broadcom Inc.
10.2. Trend Micro Incorporated
10.3. Cisco Systems, Inc.
10.4. International Business Machines Corporation (IBM)
10.5. Kaspersky
10.6. Trellix
10.7. Intel Corporation
10.8. GE HealthCare
10.9. CrowdStrike Holdings, Inc.
10.10. Imperva, Inc.
10.11. CyberArk Software Ltd.
10.12. Palo Alto Networks, Inc.
11. APPENDIX
11.1. Currency
11.2. Assumptions
11.3. Base and Forecast Years Timeline
11.4. Key Benefits for Stakeholders
11.5. Research Methodology
11.6. Abbreviations
LIST OF FIGURES
LIST OF TABLES
Navigate
Trusted by the world's leading organizations











