
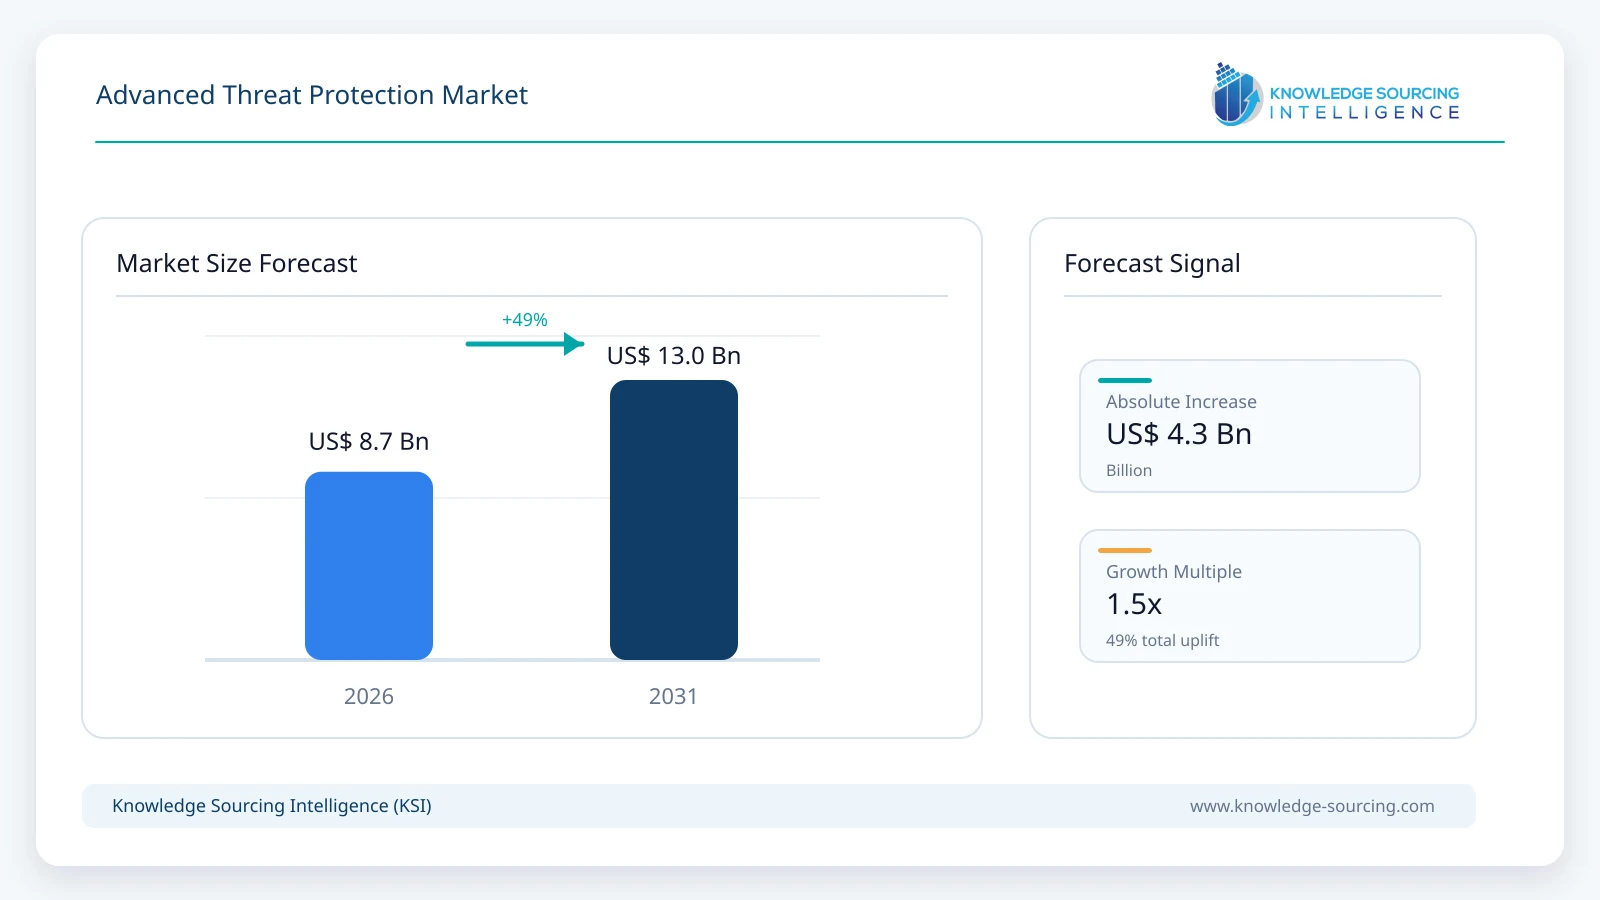
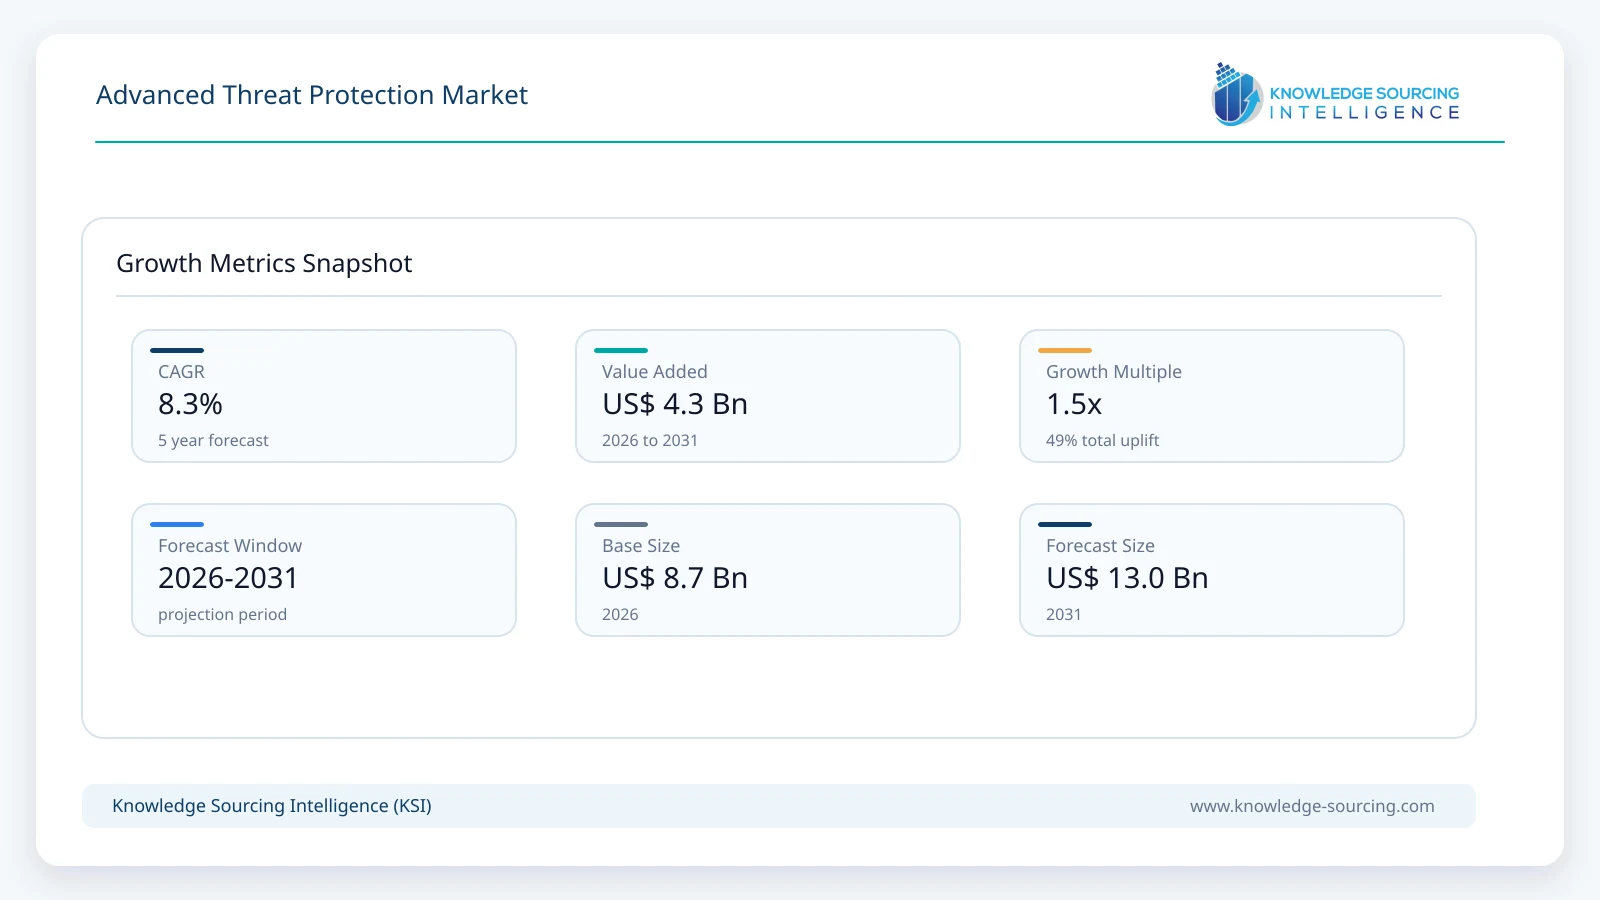
The global Advanced Threat Protection Market is expected to grow at a CAGR of 8.26%, reaching USD 13.01 billion in 2031 from an estimated USD 8.747 billion in 2026 across the forecast period.
Highlights:
- 1Malware analysis and exploit prevention remain central purchasing categories because attackers combine malicious payloads with legitimate tools and stolen credentials.
- 2Network traffic analysis is a major solution category, with inline inspection increasingly linked to threat intelligence and response workflows.
- 3Large enterprises remain the leading buyer group; medium-sized organizations increasingly obtain advanced controls through cloud delivery and managed services.
- 4Banking and financial-services organizations prioritize rapid detection validation, identity-linked investigation and incident containment across hybrid environments.
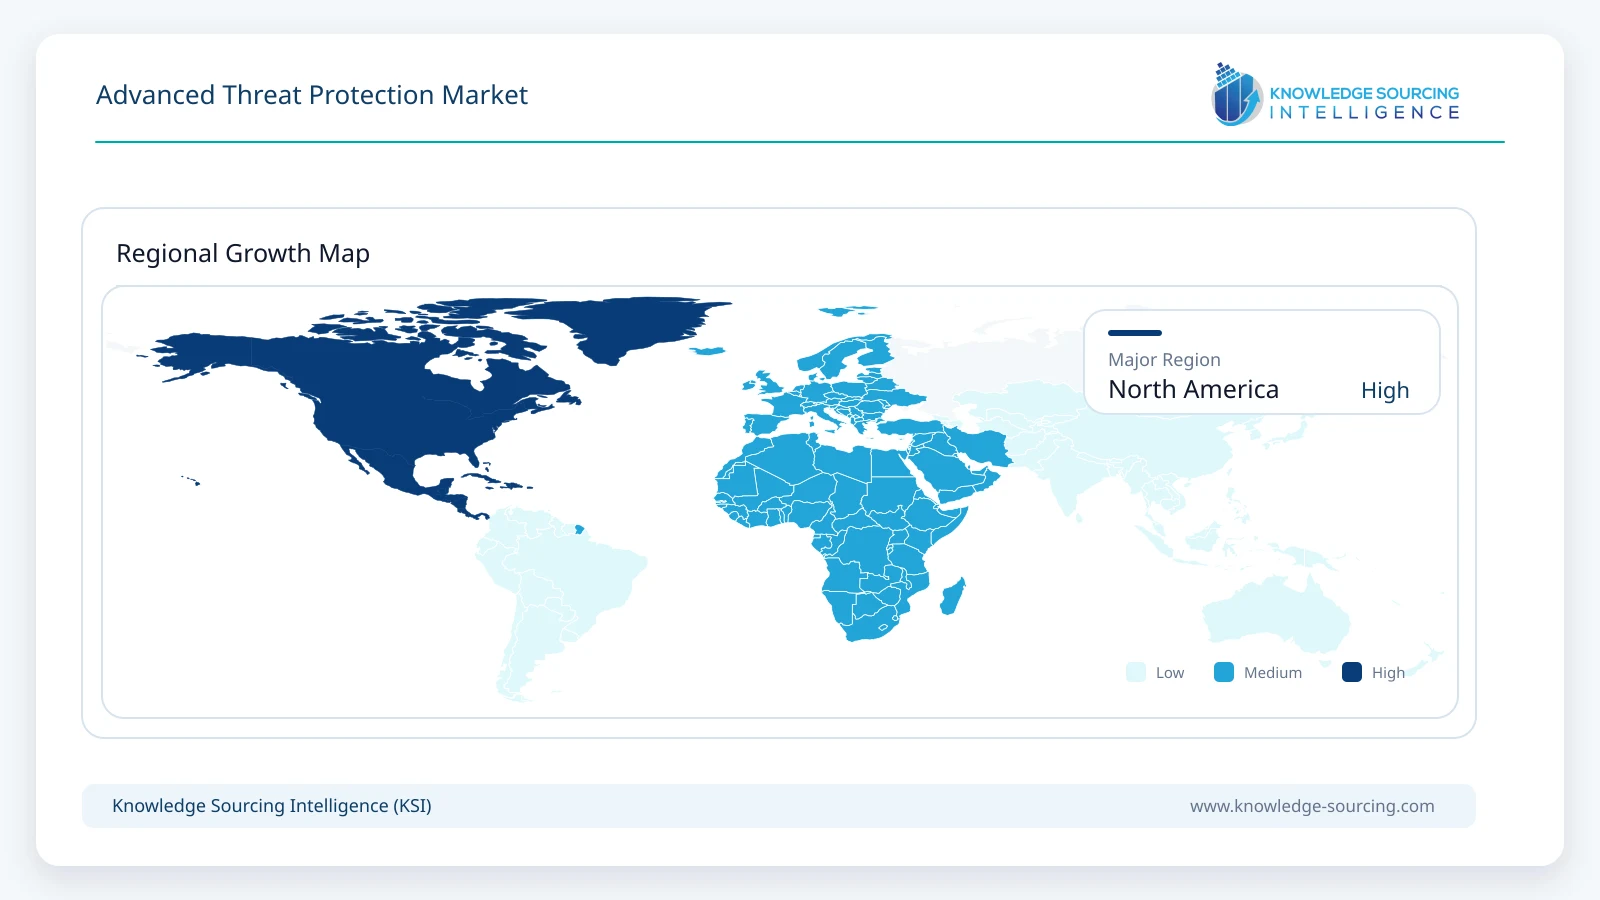
- 5North America remains the largest regional purchasing center, while Middle East and Africa shows the strongest modeled expansion as regulated digital infrastructure and managed security investment broaden.
- 6AI-assisted investigations are becoming commercially useful where detection accuracy, evidence traceability and controlled automation reduce analyst workload.
Advanced threat protection combines preventive security technologies that identify and block malicious files, exploits, command-and-control traffic and suspicious communications across enterprise networks and digital workloads. Buyers typically purchase integrated threat-prevention subscriptions, analysis platforms, cloud services and specialist deployment or response support. Network traffic analysis, sandboxing and threat intelligence sharing form the core solution categories in this market, with the mix of each service varying according to existing security architecture and exposure.
The sector increasingly relies on continuous telemetry rather than isolated inspection points. Palo Alto Networks provides inline exploit and command-and-control prevention through its Advanced Threat Prevention service; Fortinet combines FortiSandbox analysis with FortiGuard intelligence and security-fabric enforcement. Microsoft, CrowdStrike, Zscaler and Google extend prevention and investigation across endpoints, identities, cloud applications and security operations. Enterprise customers evaluate these offerings by the speed and reliability of prevention, workflow integration and the operational effort required to investigate exceptions.
Advanced persistent threats rarely rely on one malicious file or one obvious network signature. Attackers can combine exposed applications, stolen credentials, phishing messages and legitimate administration utilities to move through an organization. Security teams therefore purchase protection capable of examining payload behavior, network connections and incident context across several stages of an intrusion. The resulting market includes dedicated inspection tools as well as the attributable advanced-prevention functions sold within broader security platforms.
Palo Alto Networks uses inline deep-learning models to assess command-and-control activity and exploit attempts, while FortiSandbox analyzes unknown objects using static and dynamic techniques. Zscaler inspects cloud-routed traffic and applies policy at the connection level. Microsoft Defender XDR and CrowdStrike Falcon connect endpoint and broader security data to investigations and automated containment. The commercial distinction lies less in the use of artificial intelligence itself than in whether a vendor can enforce timely decisions across customer environments and demonstrate an acceptable false-positive rate.
Subscription delivery and cloud-assisted inspection are changing how this protection is bought. Frequent detection-model updates favor vendors with substantial threat telemetry, whereas regulated enterprises may retain local inspection for sensitive traffic or resilience requirements. Procurement increasingly compares total security-platform expenditure against the value of individual modules. Vendors with established network, endpoint or identity deployments have a distribution advantage, but focused providers can still win when they improve visibility into unmonitored traffic or reduce the work of validating complex threats.
Market Trends
Inline Prevention Moves Closer to the Point of Attack
Network prevention systems are being asked to stop exploitation at connection time rather than issue a later alert for analyst review. Palo Alto Networks markets cloud-assisted and local deep-learning analysis for unknown command-and-control behavior and zero-day exploit activity. For customers, the relevant performance measure is whether suspicious traffic can be interrupted without affecting legitimate applications or requiring burdensome manual rules.
Inline deployment changes vendor qualification. Security architects test latency, encrypted-traffic handling, policy consistency and resilience before enabling enforcement at scale. The model favors suppliers able to connect threat research with gateways, cloud edges and virtual firewalls, while maintaining clear fallback procedures when inspection services or network paths are unavailable.
Sandboxing Evolves into Integrated Malware Analysis
Sandbox products still address an important blind spot: files that appear harmless under conventional static inspection can reveal malicious behavior when executed in a controlled environment. Fortinet offers hardware, virtual, cloud and SaaS FortiSandbox options, with file behavior analysis tied to other security controls. The ability to return useful verdicts quickly is increasingly important for email, download and file-sharing workflows.
The purchasing decision is shifting from standalone detonation capacity to how effectively analysis outcomes reach enforcement points. Vendors must manage evasive samples, file-type coverage and the volume of routine submissions without imposing delays. This creates demand for tiered inspection, better pre-screening and integration with existing gateways, but limits the appeal of expensive isolated appliances in smaller deployments.
Threat Intelligence Becomes an Operational Control
Threat intelligence spending is moving beyond subscriptions to indicators and campaign reports. Security teams need evidence of exploit activity, affected assets and attack paths translated into prioritized detections or blocking actions. Google Security Operations has developed automated threat-hunting and detection-engineering capabilities, while Microsoft connects threat analytics and coordinated response within its security-operations environment. The common objective is reducing the lag between newly observed attacker methods and local defensive action.
Higher-value intelligence services are distinguished by traceable detection logic and integration quality. A feed that generates large numbers of unverified indicators can increase analyst work rather than reduce risk. Customers favor intelligence that explains confidence, supports investigation, and can be applied consistently to firewall, endpoint, cloud and identity controls.
AI-Assisted Security Operations Tighten the Prevention Loop
Integrated detection is drawing prevention and investigation into the same operating environment. CrowdStrike expanded Falcon Next-Gen SIEM in March 2026 to correlate Microsoft Defender for Endpoint telemetry without a separate Falcon sensor; Google introduced preview detection-engineering and threat-hunting agents in April. Microsoft subsequently detailed an integrated security-operations experience in September, illustrating demand for faster analysis across network, endpoint and cloud evidence. These changes matter when they reduce the time between a credible signal and an authorized prevention action, not merely when they increase the number of alerts.
Autonomous response nevertheless raises new governance requirements. An incorrect containment decision can disrupt business systems, while weak evidence chains make incident review difficult. Enterprises are therefore likely to adopt graduated automation, using high-confidence blocking for established threats and analyst confirmation for actions with broader operational consequences.
Advanced Threat Protection Market Segment Analysis
By Threat Type
Malware
Malware accounts for the largest portion of advanced threat protection spending because ransomware, information stealers, loaders and remote-access tools create direct requirements for file inspection and command-and-control blocking. Verizon’s 2025 Data Breach Investigations Report found ransomware present in 44% of reviewed breaches, providing a clear reason for continuing investment in layered preventive controls. Malware protection purchases span gateways, sandboxing services and endpoint-linked inspection rather than a single application.
The malware category is estimated to represent 51% of the 2026 market, but its share is expected to moderate as buyers increase expenditure on phishing and identity-linked attack paths. Suppliers are improving behavioral analysis, detection updates and integration with remediation workflows. Customers increasingly evaluate malware controls by missed attacks and operational disruption avoided, not by the volume of files scanned.
By Solution
Network Traffic Analysis
Network traffic analysis holds the largest solution share because encrypted applications, remote users and lateral movement produce patterns that endpoint and email controls may not observe independently. Detection of exploit traffic, abnormal connections and command-and-control channels is particularly important in complex enterprises with hybrid infrastructure. The segment is modeled at approximately 39% of market revenue in 2026.
Palo Alto Networks, Fortinet and Cisco compete partly through their established network-security footprint, while cloud-security providers can analyze traffic routed through their services. Investment decisions involve throughput, coverage of east-west and internet-bound connections, and the ability to enforce verdicts promptly. Network analytics also faces a privacy and compute trade-off as encryption limits payload access and increases the value of metadata and behavior.
By Enterprise Size
Large Enterprises
Large enterprises account for an estimated 65% of 2026 expenditure, reflecting multi-site networks, differentiated cloud environments and security operations centers that routinely handle large telemetry volumes. These organizations commonly buy a portfolio of subscriptions and specialist integrations rather than one basic protection package. Contract value depends on licensed assets, inspection capacity, data retention and managed capabilities.
Their bargaining power is substantial, with requirements for product interoperability, regional data handling, documented detection performance and platform availability. At the same time, complex estates make it difficult to switch vendors quickly. Medium-sized organizations are expected to grow faster from a smaller base where cloud inspection and managed detection reduce the need for substantial in-house expertise.
By End User
Banking, Financial Services and Insurance
Banks, insurers and payment businesses are intensive users of advanced threat protection because interruption, unauthorized transfers and compromise of customer information can generate immediate financial and regulatory consequences. Application exposure, phishing and supplier access are major purchasing concerns. In the European Union, the Digital Operational Resilience Act became applicable in January 2025, reinforcing formal management of ICT operational risk and third-party resilience.
The BFSI segment is estimated at 27% of 2026 market value. Spending is directed toward network and application prevention, behavioral monitoring, incident investigation and evidence needed for control assurance. Vendors that join preventive telemetry to regulated operational workflows are well placed, although customer testing, change-management procedures and long procurement cycles can delay deployment.
Market Drivers
Exploitation of Internet-Facing Vulnerabilities
Attackers continue to use vulnerable gateways, public applications and remote-access services as initial entry points. Verizon reported that vulnerability exploitation accounted for 20% of selected breach access vectors in its 2025 investigation, while IBM’s 2026 X-Force review identified public-facing application exploitation as a leading entry method in its incident sample. These findings favor network inspection and rapid detection-rule updates.
Organizations purchase advanced prevention when patching is slower than active exploitation or when an exposed device cannot be taken offline immediately. Suppliers that combine exploit intelligence with enforceable policies can capture subscription expenditure alongside existing firewall investments. Protection remains complementary to patch management, not a replacement for it.
Ransomware and Multi-Stage Malware Attacks
Ransomware campaigns commonly combine credential access, malicious tooling and lateral movement before encryption or extortion. This sequence gives several opportunities for detection but also requires controls that exchange useful context. Behavioral malware analysis, unusual traffic detection and command-and-control prevention are consequently purchased as connected functions rather than independent products.
Insurers, manufacturers and critical-service operators prioritize containment of business interruption, not simply the removal of infected files. Demand supports multi-year protection subscriptions and managed response offerings. However, buyers increasingly ask vendors to demonstrate measurable reduction in escalation time and operational exposure rather than relying only on laboratory detection claims.
Expansion of Cloud and Remote Access Environments
Enterprise applications and workforce access are distributed across data centers, cloud platforms, branches and third-party connections. A control situated only at the corporate perimeter cannot inspect all relevant traffic. Cloud-delivered security and distributed inspection therefore widen the commercial addressable base for advanced protection, especially where customers already operate multiple identity and endpoint tools.
Subscription-based services allow vendors to extend inspection without matching every new site to a dedicated appliance purchase. Integration cost still matters: buyers must map traffic routing, local data requirements and enforcement responsibilities before enabling services. Vendors with interoperable cloud connectors and predictable operating costs are better placed to convert deployment into recurring revenue.
Regulatory Scrutiny and Resilience Requirements
Financial-sector resilience expectations and broader critical-infrastructure requirements are reinforcing investment in detection, incident handling and controls assurance. DORA applies to European financial entities, while cyber authorities such as CISA and ENISA continue publishing operational threat information. These developments strengthen the case for products that preserve evidence, support investigation and show how rapidly threats are contained.
Compliance alone does not prescribe a single advanced threat protection platform. The commercial effect is instead greater scrutiny of control effectiveness and third-party dependencies. Vendors that document integrations, response processes and deployment assurance are more likely to satisfy regulated procurement processes than suppliers offering detection performance claims without operational proof.
Security-Team Capacity and Managed Delivery
Security teams face growing volumes of alerts, specialist tooling and fragmented incident evidence. Automated file analysis, enrichment and investigation reduce the time analysts spend separating genuine attacks from routine events. Microsoft, CrowdStrike and Google are building these functions into broader security-operations offerings, making operational productivity part of the competitive comparison.
Medium-sized companies can gain access through managed services rather than staffing a full internal response function. This supports growth in packaged subscriptions and outsourced delivery, although providers must price services against the number of protected assets and the expected investigation workload. Accurate triage is particularly valuable when personnel remain the binding constraint.
Market Restraints
False Positives and Business Disruption
Advanced prevention tools make decisions on incomplete signals, and blocking a legitimate file, connection or user process can interrupt production services. The risk is greater when enforcement extends across payments, industrial workloads or high-availability applications. Buyers therefore require pilot deployments, exception procedures and evidence that detection improvements do not create unacceptable operational costs.
Automated response is frequently introduced in stages, beginning with monitoring and progressing to selective enforcement. This lengthens qualification and can limit the adoption rate of the most aggressive protective functions. Suppliers with explainable decisions, tunable thresholds and reliable rollback controls have an advantage over models that return an opaque block verdict.
Complex Integration Across Security Architectures
Enterprises rarely replace network, endpoint, identity, email and cloud systems at the same time. Advanced protection must consequently work across multiple consoles, log formats and enforcement policies. The cost of translating telemetry, adjusting workflows and maintaining integrations can be material even when the software subscription appears affordable.
Platform consolidation can reduce some complexity but may create dependencies on a single vendor and complicate future procurement. Open telemetry and third-party connectors are therefore important purchasing criteria. Companies with older applications or heavily customized networks may defer broad deployment until a staged integration plan is available.
High Inspection and Data-Processing Costs
Deep file analysis, encrypted-traffic inspection and long-term threat telemetry require compute capacity, network bandwidth and storage. High-volume industries must decide which objects and connections deserve the most intensive examination. An architecture that sends every event to expensive analysis can produce costs that outweigh the additional protection gained.
Vendors are responding with pre-filtering, selective detonation and cloud-based analysis, but customers still compare incremental value against existing platform features. Data-egress charges and regional storage restrictions can further complicate cloud delivery. These economics are most restrictive for smaller customers and high-throughput environments with limited security budgets.
Shortage of Experienced Detection and Response Personnel
Advanced threat protection requires practitioners who can tune policies, interpret suspicious behavior and assess whether containment decisions are justified. Skilled analysts are difficult to replace with technology when incidents involve unfamiliar systems or competing business priorities. An organization may own capable tools without realizing their protective value if alerts are not investigated consistently.
Managed services and automated triage help alleviate the constraint but do not eliminate customer responsibility for security architecture and escalation decisions. Procurement projects can stall when enterprises lack the staff to implement complex controls. Suppliers that provide training, clear workflows and reliable third-party service integration are better positioned to convert purchases into effective usage.
Encrypted Traffic, Privacy and Data Sovereignty
Modern protocols and widespread encryption restrict inspection of message content, while regulatory and contractual obligations constrain where sensitive logs can be processed. Full decryption is often undesirable for privacy, performance or application-compatibility reasons. Threat protection consequently must rely more heavily on connection behavior, reputation, local analysis and endpoint context.
Multinational organizations often require separate operating models for different jurisdictions and workloads. These constraints increase implementation expense and can delay cloud-only deployments. Suppliers offering regional processing options, transparent telemetry controls and effective inspection without indiscriminate decryption are likely to compete more effectively for regulated accounts.
Regional Outlook
North America
North America is the largest advanced threat protection region, supported by substantial enterprise technology expenditure, a concentration of global vendors and extensive financial, government and digital-service infrastructure. The region is estimated to represent 36% of market value in 2026. Public reporting from Verizon and IBM continues to document vulnerability exploitation, ransomware and third-party exposure, providing security buyers with operational evidence for layered protection.
The United States accounts for most regional purchasing, with procurement extending from large integrated platforms to specialist security-services providers. Strong demand does not guarantee easy market entry: regulated clients expect audited controls, proven interoperability and dependable support. Competition increasingly centers on bundled prevention, threat research and incident operations rather than appliances alone.
Middle East and Africa
Middle East and Africa is expected to register the fastest growth among the main regions, albeit from a smaller spending base than North America or Europe. Government digital services, financial infrastructure and connected industrial assets are expanding the number of systems that require exploit prevention, suspicious-traffic analysis and applied threat intelligence. Saudi Arabia’s National Cybersecurity Authority maintains Essential Cybersecurity Controls for national entities and critical infrastructure operators, giving security procurement a defined governance and assurance context. Cloud migration and regional data-center development create additional demand for protection that can operate across public services, enterprise networks and hosted applications.
Procurement conditions differ across the Gulf states and African economies. Large public and financial buyers can support integrated monitoring and specialist sandboxing, whereas resource-constrained organizations often rely on managed services and subscription bundles. Vendors pursuing regional growth must demonstrate effective deployment through local partners, predictable inspection performance and compliance with customer data-handling requirements. Growth prospects are attractive, but long qualification processes and shortages of experienced security engineers can delay the conversion of infrastructure expenditure into recurring advanced-prevention subscriptions.
Competitive Landscape
Competition is divided among network-security vendors, cloud-delivered inspection specialists and broader security-operations platforms. Palo Alto Networks and Fortinet link threat prevention to firewall estates and their threat research services; Check Point competes through integrated network and cloud prevention. Cisco combines networking and security capabilities, while HPE now owns Juniper Networks following the July 2025 acquisition. These firms retain access to customers through deployed gateways, policy management and enterprise distribution channels.
Zscaler and Microsoft compete through cloud inspection, identity-connected signals and broad subscription platforms. CrowdStrike uses endpoint telemetry and cross-domain investigation, while Google combines security operations with Mandiant-derived intelligence and cloud tooling. Trend Micro, Sophos and Broadcom also participate through malware, endpoint, email and network protection portfolios. Product overlap is significant, so broad company revenue cannot be read directly as this market’s share.
Winning propositions typically combine prevention efficacy, predictable performance and lower investigation effort. Buyers also distinguish products that can enforce real-time policy from tools focused mainly on recording or correlating events. The market is likely to favor vendors with credible threat telemetry and deployable integrations, although specialist vendors can remain competitive in sandboxing, network analytics or regulated environments where platform suites leave coverage gaps.
Recent Developments
February 2026: Microsoft and CrowdStrike expanded their alliance so customers could procure the CrowdStrike Falcon platform through Microsoft Marketplace using eligible Azure consumption commitments. The announcement concerns procurement access, not a new protection algorithm.
March 2026: CrowdStrike announced support for Microsoft Defender for Endpoint telemetry in Falcon Next-Gen SIEM, enabling cross-vendor correlation without installing a Falcon endpoint sensor for that use case.
April 2026: Google Cloud introduced Threat Hunting and Detection Engineering agents in Google Security Operations as preview capabilities intended to support investigation and coverage-gap identification.
June 2026: Zscaler announced Zero Trust Exchange product innovations designed to govern how enterprise AI agents connect to systems, interact with data and run on devices.
August 2026: Fortinet announced the completed acquisition of Virtue AI, expanding its capabilities in AI application validation and runtime protection; the transaction alone does not demonstrate installed ATP revenue.
September 2026: Microsoft introduced an integrated security-operations experience in Defender, bringing together extended detection, SIEM, threat intelligence and automation for eligible customers; some functions were initially preview features.
Market Outlook
Advanced threat protection expenditure is expected to rise as attackers continue to exploit external applications, stolen credentials and gaps between network and endpoint controls. The market will not grow uniformly across its technologies. Inline inspection, applied threat intelligence and cloud-delivered detection should gain emphasis where they support prevention decisions that can be made before an intrusion spreads.
Security vendors are likely to package a greater share of specialist prevention functions within broader subscriptions. This creates competitive pressure for independent products but can expand adoption among customers without dedicated security engineering teams. Large enterprises will continue to demand detailed interoperability, testing and operational evidence, while medium-sized customers increasingly favor managed delivery and simplified contracts.
Over the forecast period, the commercial differentiation will shift toward demonstrable reduction in attack exposure, dependable automation and restrained inspection costs. North America should remain the largest purchasing center, with the fastest modeled regional growth in Middle East and Africa. Vendors that reconcile prevention accuracy, customer data controls and operational complexity will be better positioned than those competing only on the number of alerts or models deployed.
Advanced Threat Protection Market Scope:
| Report Metric | Details |
|---|---|
| Total Market Size in 2026 | USD 8.747 billion |
| Total Market Size in 2031 | USD 13.01 billion |
| Forecast Unit | USD Billion |
| Growth Rate | 8.26% |
| Study Period | 2021 to 2031 |
| Historical Data | 2021 to 2024 |
| Base Year | 2025 |
| Forecast Period | 2026 – 2031 |
| Segmentation | Threat Type, Solution, Enterprise Size, End User, Geography |
| Companies |
|
| Customization Scope | 15% Free Customization included with purchase — Request Custom Breakdown → |
| Sample & Data Access | PDF Sample, Excel Databook & Analyst Briefing — Download Free Sample → |
Market Segmentation
By Threat Type
Malware
Spyware
Phishing
Others
By Solution
Network Traffic Analysis
Sandboxing
Threat Intelligence Sharing
Others
By Enterprise Size
Small
Medium
Large
By End User
BFSI
IT & Telecommunication
Government
Healthcare
Clinics
Others
By Geography
North America
United States
Canada
Mexico
South America
Brazil
Argentina
Others
Europe
United Kingdom
Germany
France
Spain
Others
Middle East and Africa
Saudi Arabia
UAE
Others
Asia Pacific
China
Japan
India
South Korea
Australia
Others
Table of Contents
1. EXECUTIVE SUMMARY
1.1. Key Findings
1.2. Global Market Outlook, 2026–2031
1.3. Segment and Regional Opportunity Summary
2. MARKET SNAPSHOT
2.1. Market Overview
2.2. Market Definition
2.3. Scope of the Study
2.4. Market Segmentation
3. BUSINESS LANDSCAPE
3.1. Market Drivers
3.1.1. Exploitation of Internet-Facing Vulnerabilities
3.1.2. Ransomware and Multi-Stage Malware Attacks
3.1.3. Expansion of Cloud and Remote Access Environments
3.1.4. Regulatory Scrutiny and Resilience Requirements
3.1.5. Security-Team Capacity and Managed Delivery
3.2. Market Restraints
3.2.1. False Positives and Business Disruption
3.2.2. Complex Integration Across Security Architectures
3.2.3. High Inspection and Data-Processing Costs
3.2.4. Shortage of Experienced Detection and Response Personnel
3.2.5. Encrypted Traffic, Privacy and Data Sovereignty
3.3. Market Opportunities
3.4. Porter’s Five Forces Analysis
3.5. Industry Value Chain Analysis
3.6. Policies and Regulations
3.7. Strategic Recommendations
4. TECHNOLOGICAL OUTLOOK
4.1. Inline Deep-Learning Intrusion Prevention
4.2. Dynamic Malware Sandboxing
4.3. Network Traffic and Behavioral Analytics
4.4. Threat Intelligence Enrichment
4.5. Automated Incident Containment
4.6. Cloud-Based Security Inspection
5. ADVANCED THREAT PROTECTION MARKET BY THREAT TYPE
5.1. Introduction
5.2. Malware
5.3. Spyware
5.4. Phishing
5.5. Others
6. ADVANCED THREAT PROTECTION MARKET BY SOLUTION
6.1. Introduction
6.2. Network Traffic Analysis
6.3. Sandboxing
6.4. Threat Intelligence Sharing
6.5. Others
7. ADVANCED THREAT PROTECTION MARKET BY ENTERPRISE SIZE
7.1. Introduction
7.2. Small
7.3. Medium
7.4. Large
8. ADVANCED THREAT PROTECTION MARKET BY END USER
8.1. Introduction
8.2. BFSI
8.3. IT & Telecommunication
8.4. Government
8.5. Healthcare
8.6. Clinics
8.7. Others
9. ADVANCED THREAT PROTECTION MARKET BY GEOGRAPHY
9.1. Introduction
9.2. North America
9.2.1. United States
9.2.2. Canada
9.2.3. Mexico
9.3. South America
9.3.1. Brazil
9.3.2. Argentina
9.3.3. Others
9.4. Europe
9.4.1. United Kingdom
9.4.2. Germany
9.4.3. France
9.4.4. Spain
9.4.5. Others
9.5. Middle East and Africa
9.5.1. Saudi Arabia
9.5.2. UAE
9.5.3. Others
9.6. Asia Pacific
9.6.1. China
9.6.2. Japan
9.6.3. India
9.6.4. South Korea
9.6.5. Australia
9.6.6. Others
10. COMPETITIVE ENVIRONMENT AND ANALYSIS
10.1. Major Players and Strategy Analysis
10.2. Market Share Analysis
10.3. Mergers, Acquisitions, Agreements and Collaborations
10.4. Competitive Dashboard
11. COMPANY PROFILES
11.1. Palo Alto Networks, Inc.
11.2. Microsoft Corporation
11.3. Fortinet, Inc.
11.4. Check Point Software Technologies Ltd.
11.5. Zscaler, Inc.
11.6. CrowdStrike Holdings, Inc.
11.7. Cisco Systems, Inc.
11.8. Trend Micro Incorporated
11.9. Broadcom Inc.
11.10. Hewlett Packard Enterprise Company
11.11. Google LLC
11.12. Sophos Limited
12. APPENDIX
12.1. Currency
12.2. Assumptions
12.3. Base and Forecast Years Timeline
12.4. Key Benefits for Stakeholders
12.5. Research Methodology
12.6. Abbreviations





Frequently asked questions
What is the projected market size for Advanced Threat Protection by 2031?
The Advanced Threat Protection Market is projected to reach USD 13.01 billion by 2031.
What is the projected Compound Annual Growth Rate (CAGR) for the market?
The Advanced Threat Protection Market is expected to grow at an 8.26% CAGR.
Which region is the largest purchasing center in the ATP market?
North America remains the largest regional purchasing center.
Which region shows the strongest expansion in Advanced Threat Protection?
Middle East and Africa shows the strongest modeled expansion.
What are the core solution categories in Advanced Threat Protection?
Network traffic analysis, sandboxing, and threat intelligence sharing.
Which buyer group leads the Advanced Threat Protection market?
Large enterprises remain the leading buyer group.
Cite this report
Knowledge Sourcing Intelligence. (Oct 2026). Advanced Threat Protection Market - Strategic Insights and Forecasts (2026-2031). https://www.knowledge-sourcing.com/report/advanced-threat-protection-market